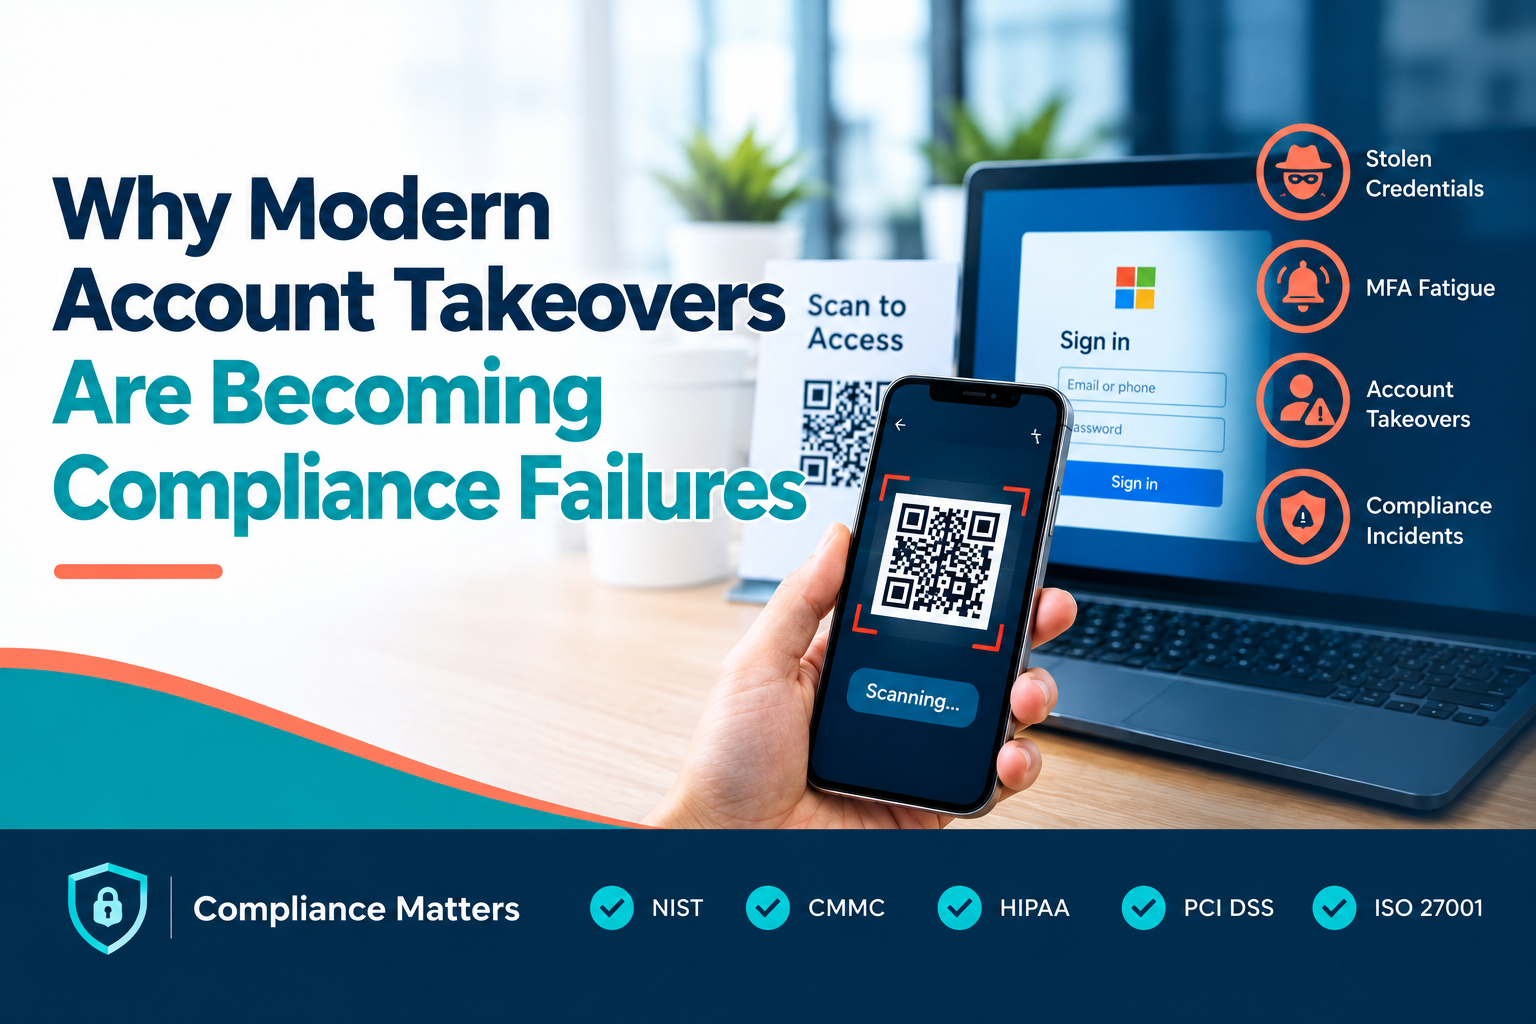
When MFA Isn't Enough: The Compliance Risks Behind QR Code Phishing and Modern Account Takeovers
For years, organizations have been told that enabling multi-factor authentication (MFA) is one of the most effective ways to protect user accounts.
And it is.
But today's attackers are no longer focused on breaking technology. They are focused on exploiting people.
Instead of guessing passwords or launching sophisticated technical attacks, cybercriminals are taking advantage of everyday actions employees perform without a second thought—scanning a QR code, approving a login request, or granting access to a seemingly legitimate application.
As a result, organizations that believe they have strong authentication controls in place are still experiencing account compromises, business email fraud, data exposure incidents, and compliance failures.
This is no longer just a cybersecurity problem.
It is a compliance problem.
Because when an employee account is compromised, auditors, regulators, clients, insurers, and business partners are not interested in whether MFA was enabled. They want to know whether your organization had effective controls in place to prevent, detect, and respond to the threat.