The Human Factor in Cybersecurity: How Small Businesses Can Reduce Insider Threats and Compliance Risks
Why employee awareness, documented policies, and effective internal controls are essential to protecting business data.
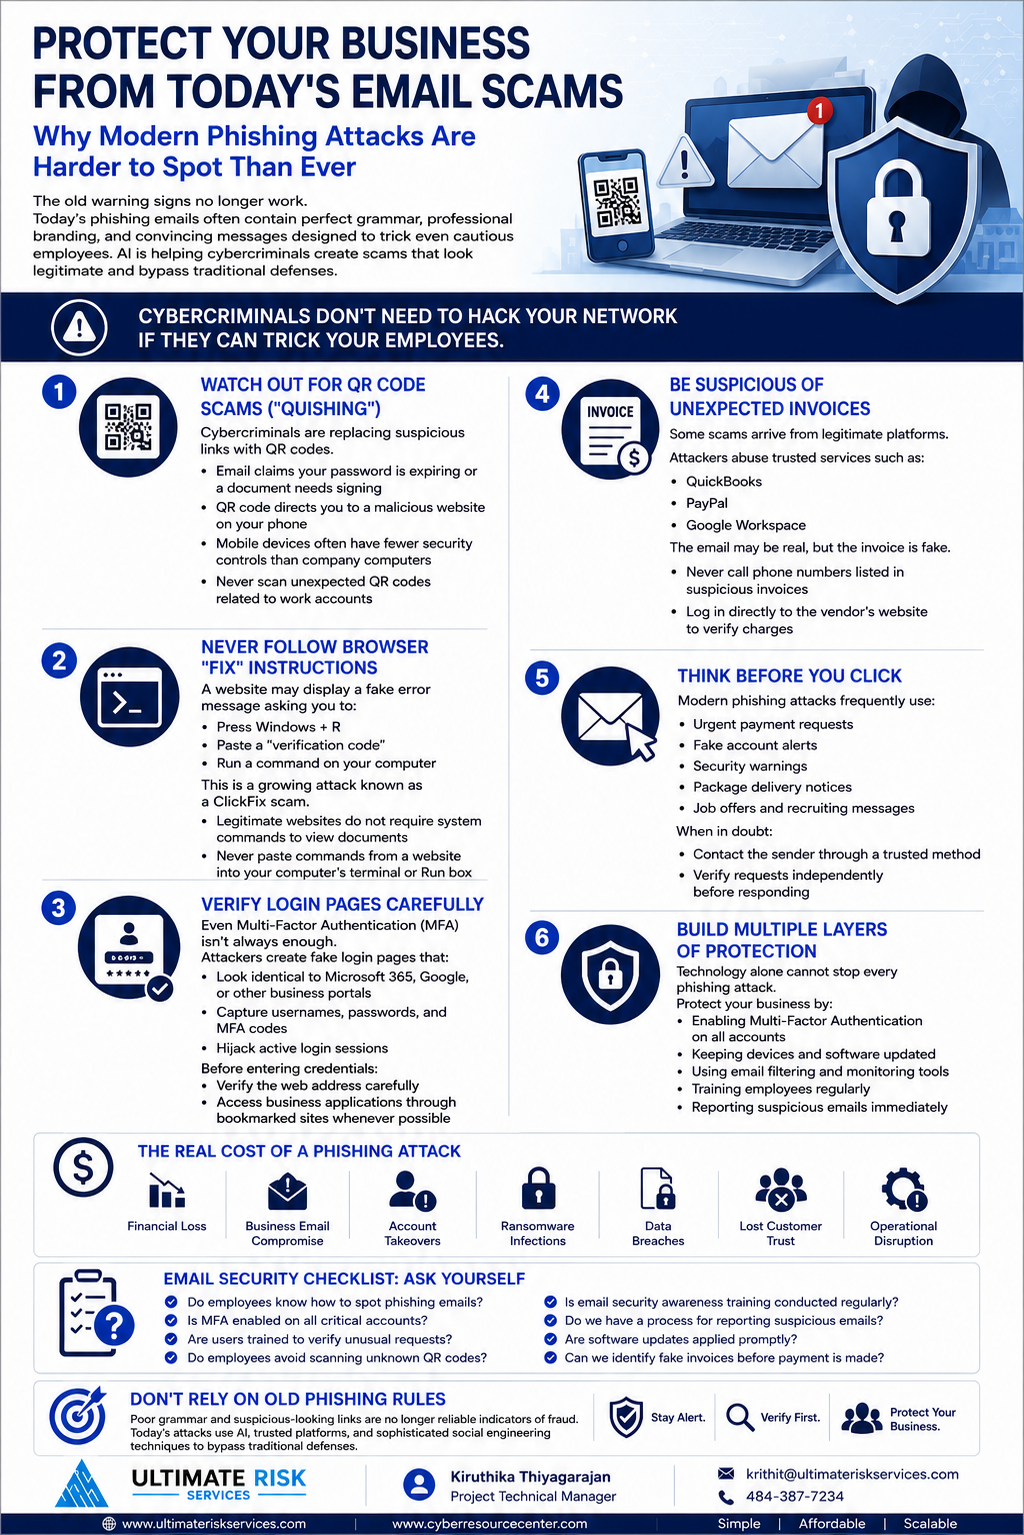
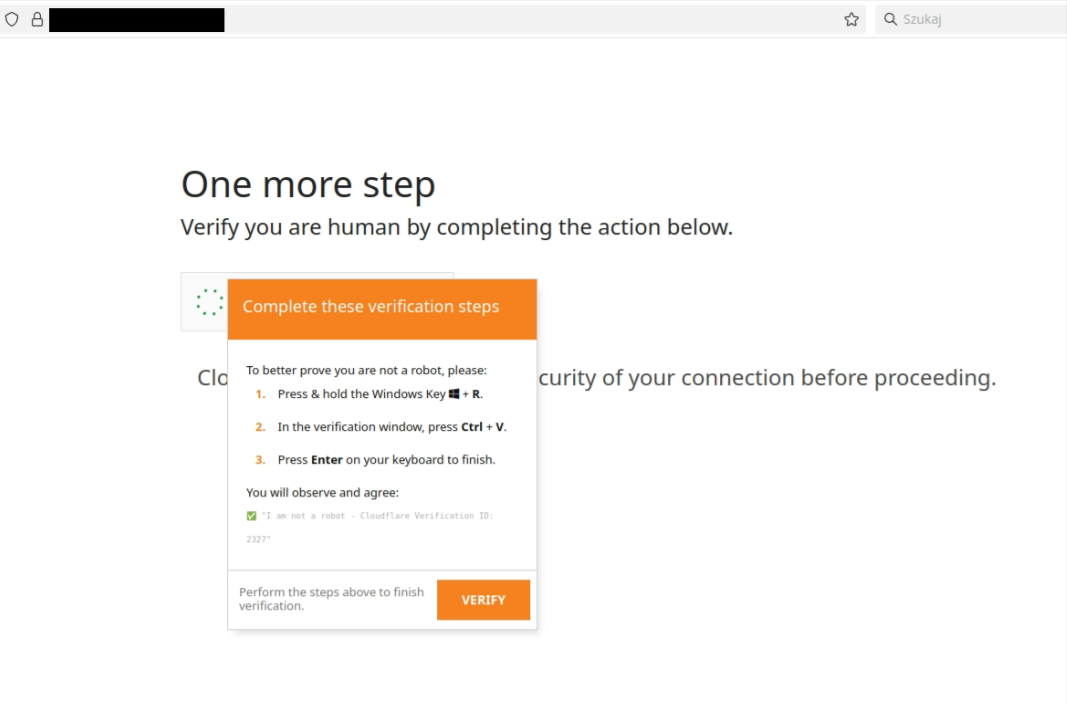
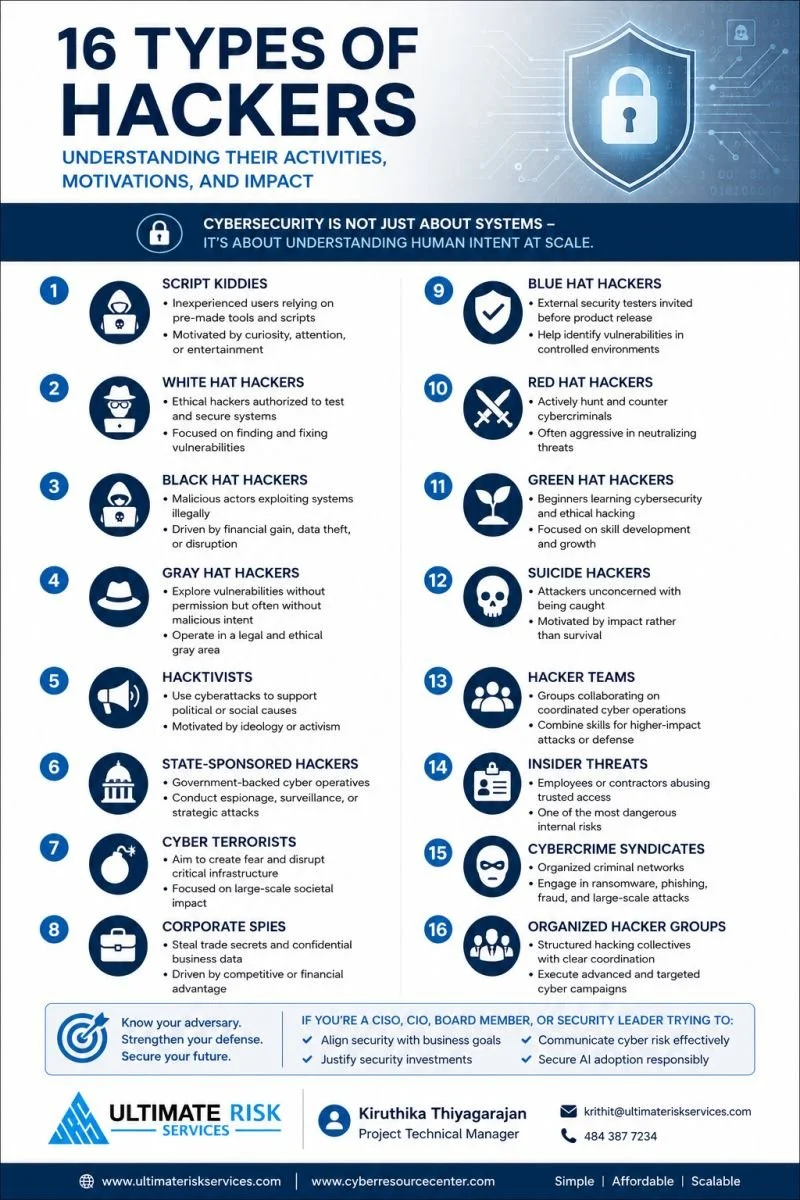
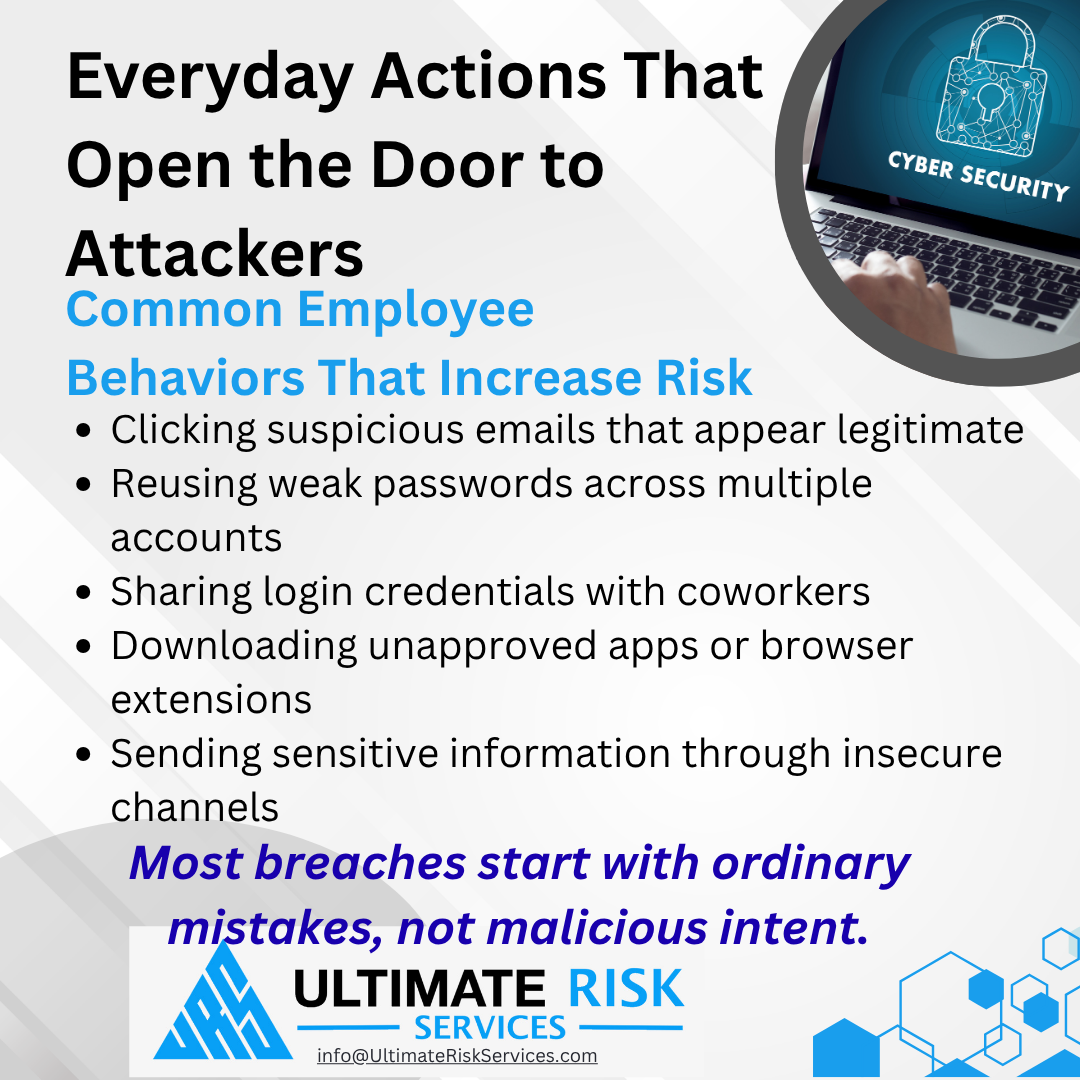
Cybersecurity incidents do not always begin with sophisticated hackers breaking through advanced security systems. Sometimes, they start with an employee clicking a fraudulent email link, sharing sensitive information with the wrong person, reusing a compromised password, or downloading unauthorized software.
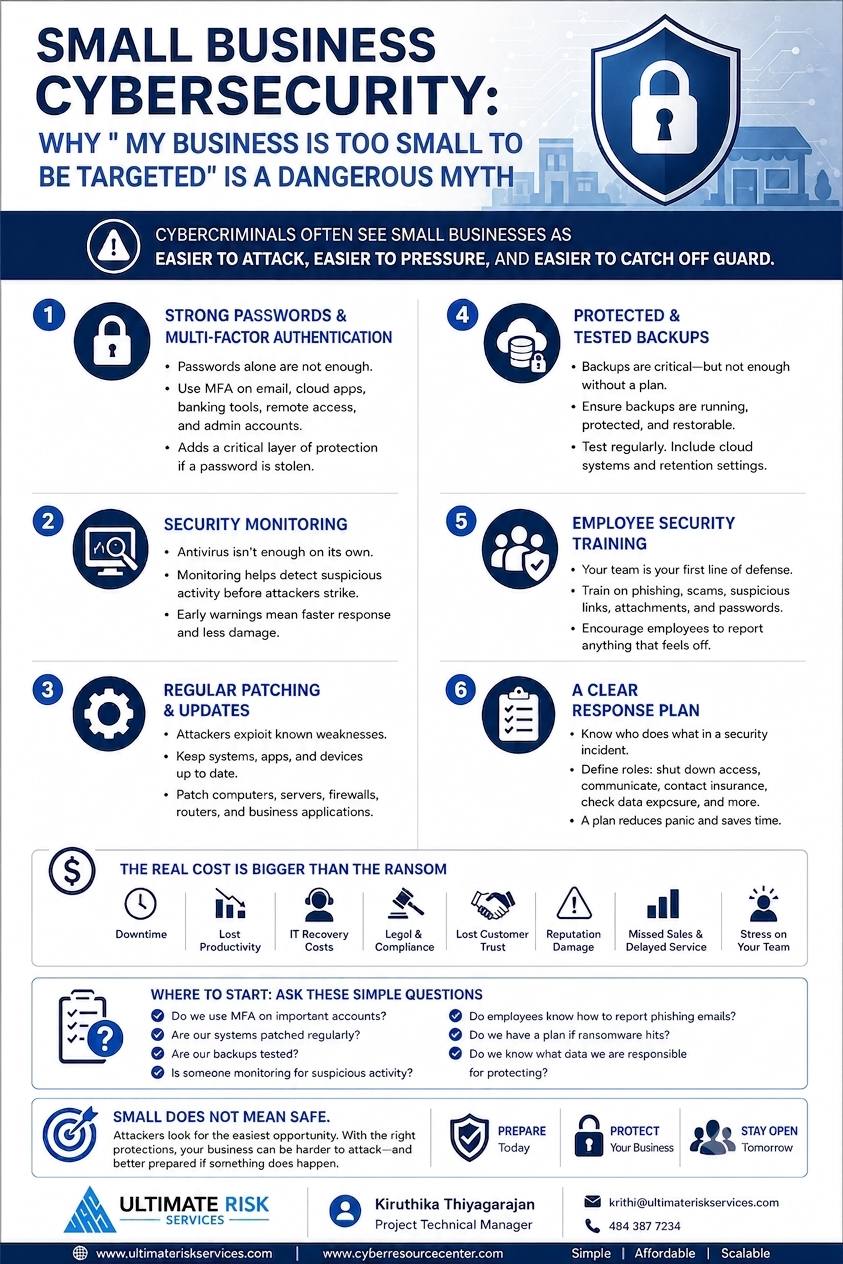
For small businesses, these seemingly minor actions can lead to significant consequences, including data breaches, operational disruptions, financial losses, and regulatory compliance issues.
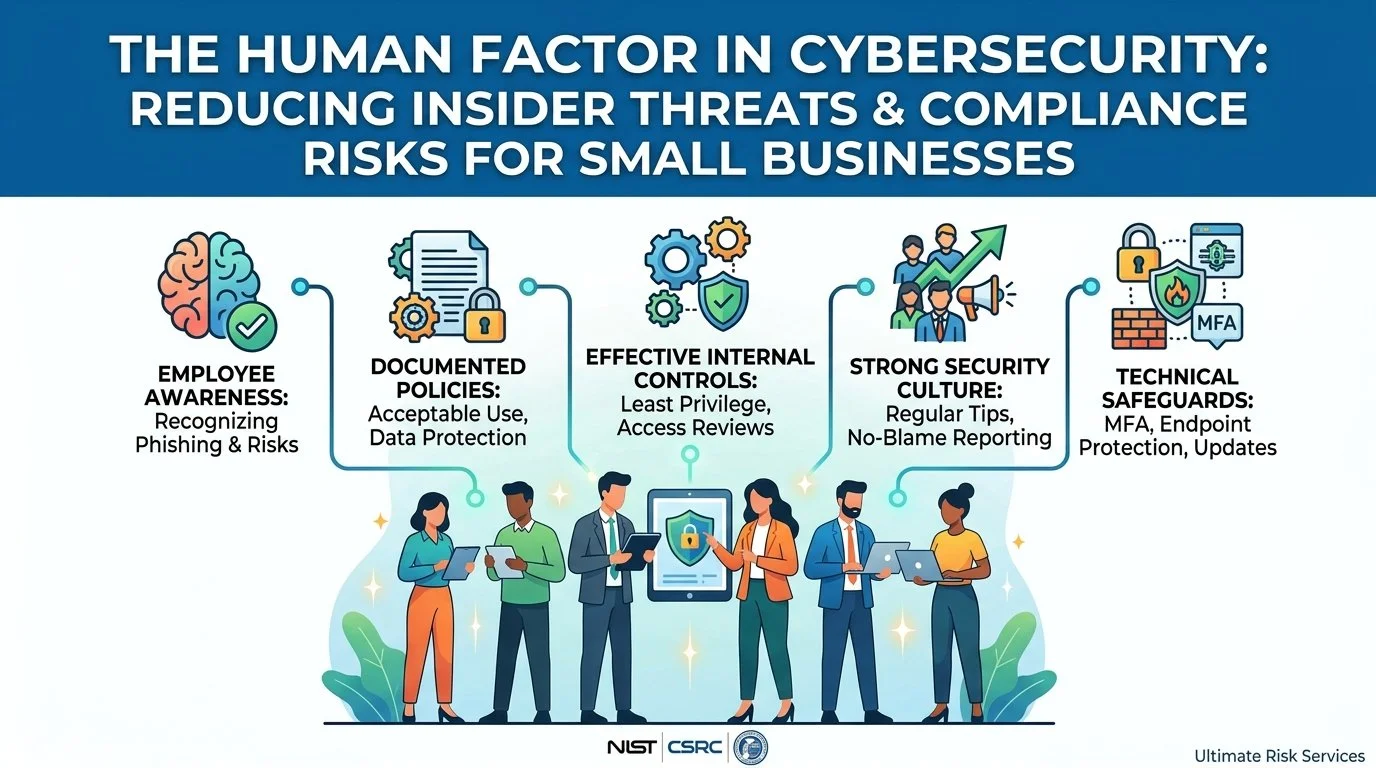
Employees are not necessarily the enemy. In many cases, they are the first line of defense against cyber threats. The challenge is ensuring they understand their responsibilities, recognize potential risks, and follow established security procedures.
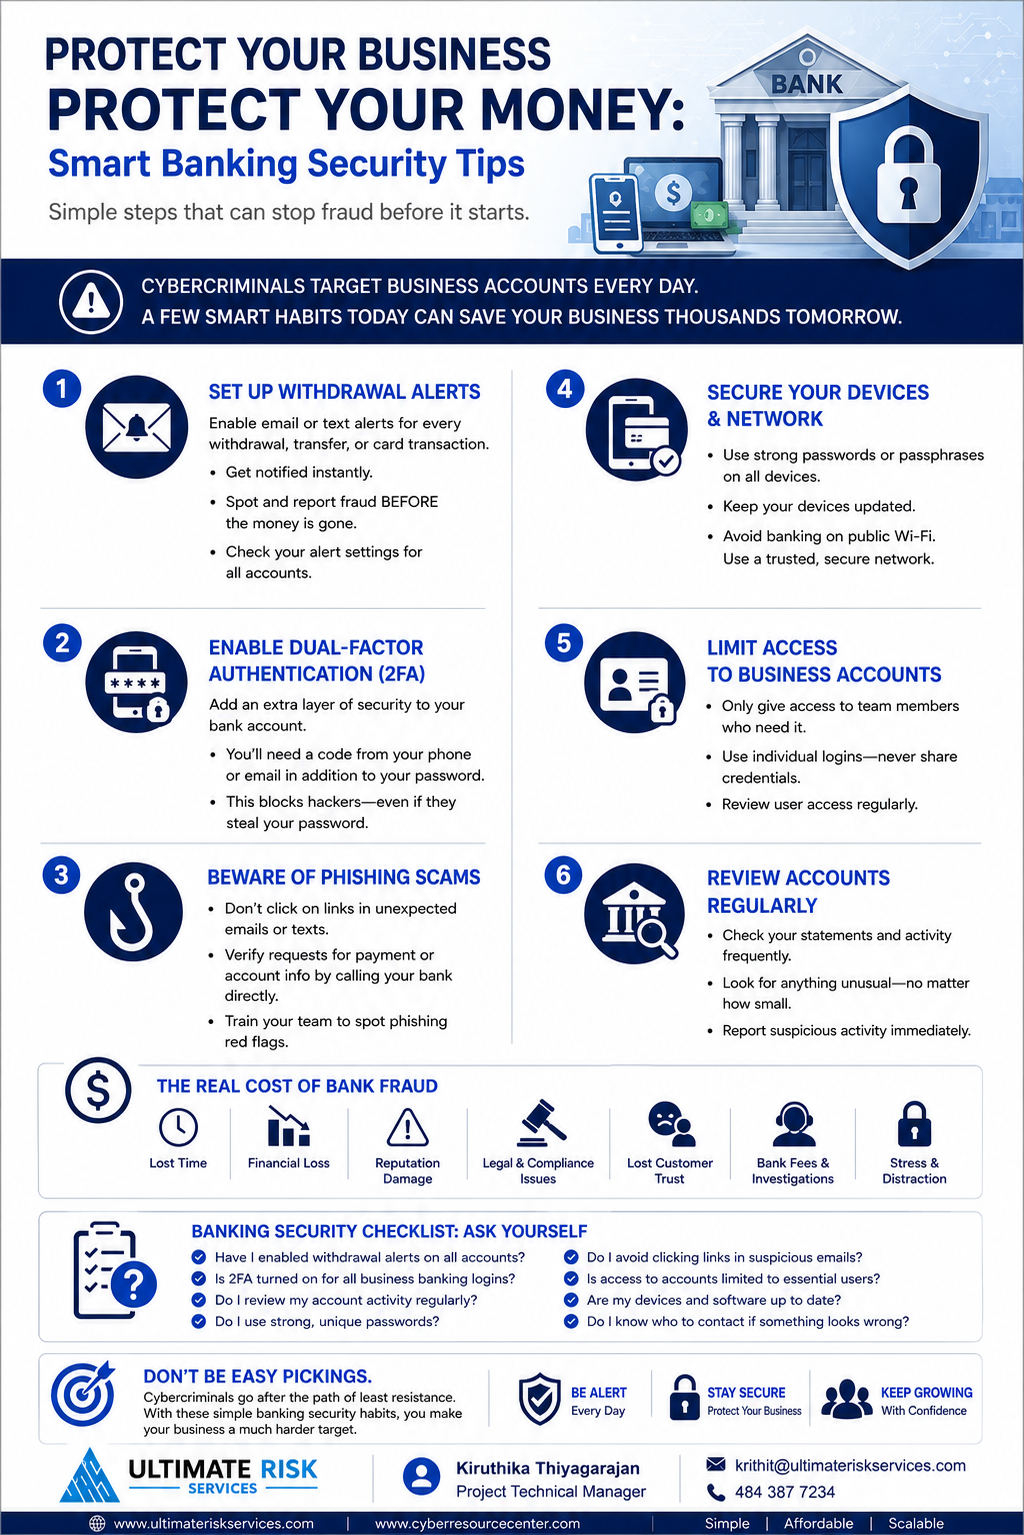
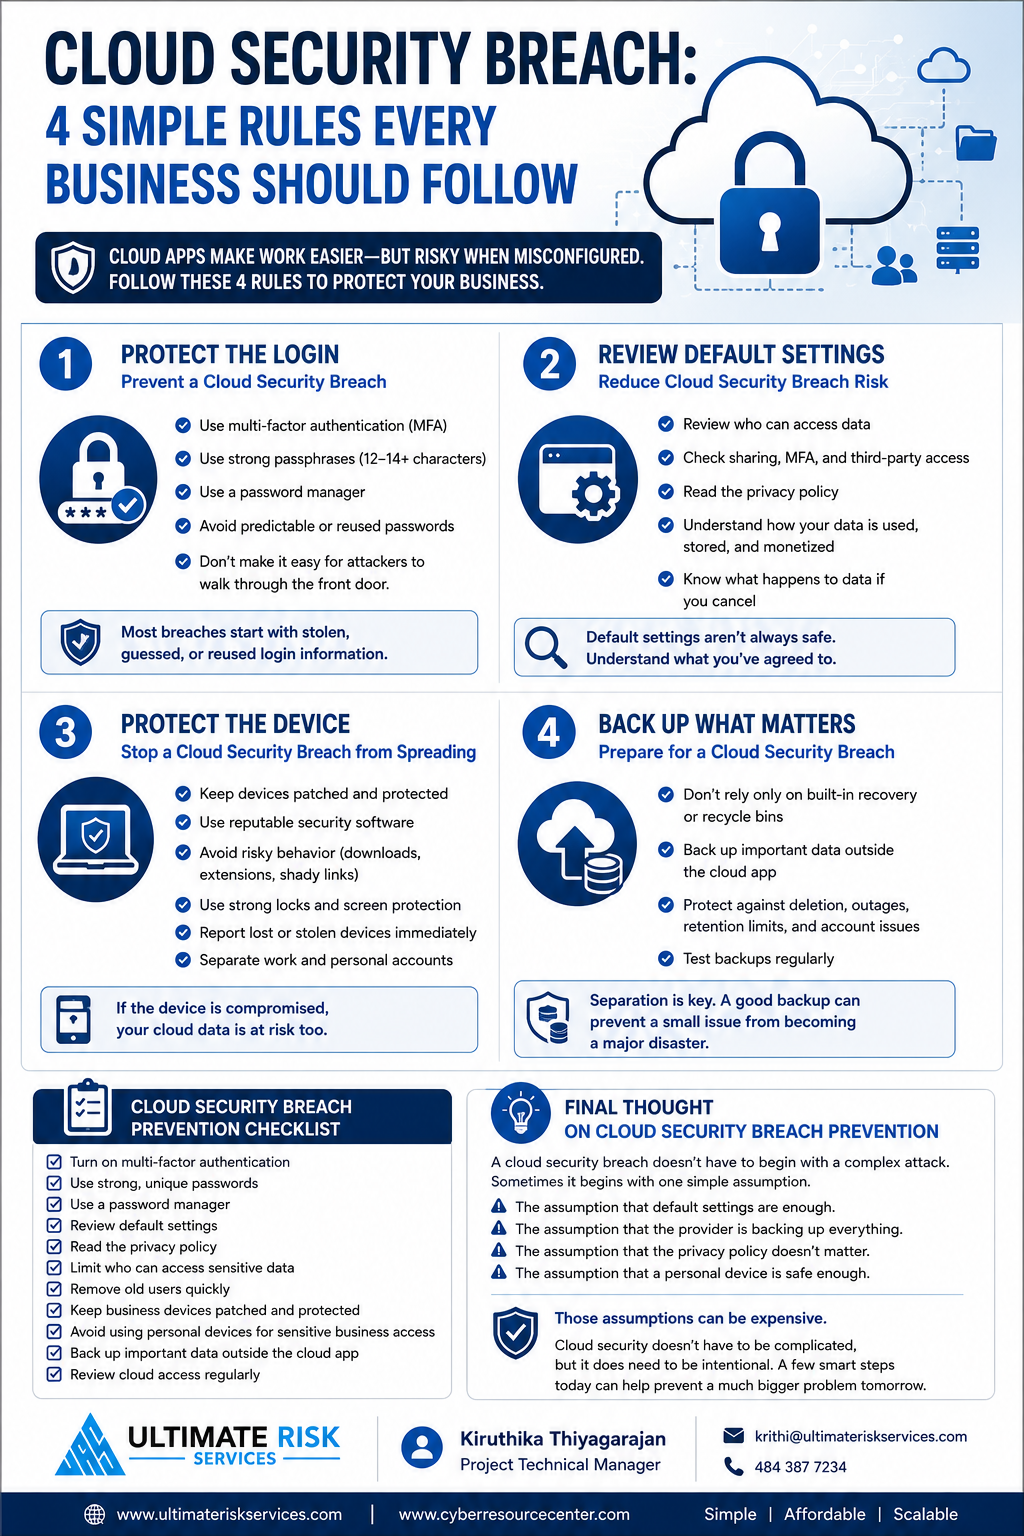
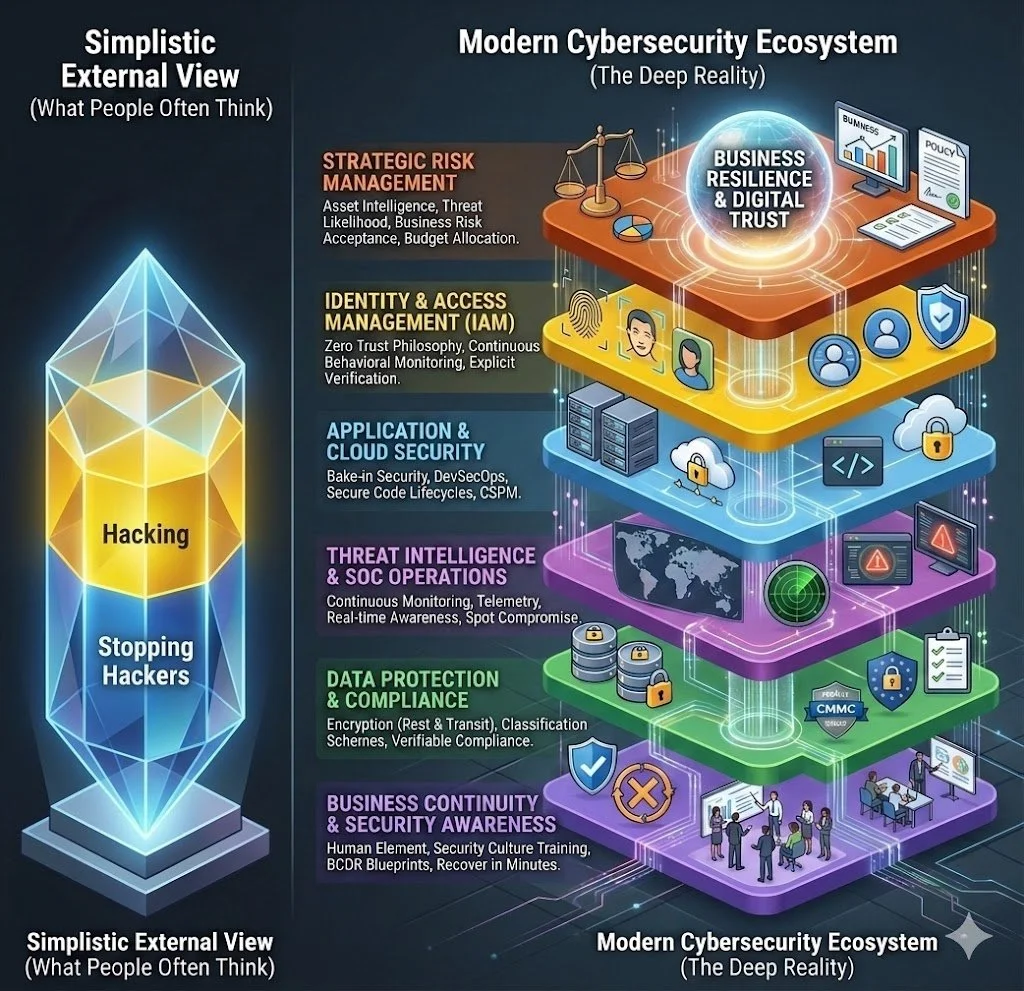
From a cybersecurity compliance perspective, protecting an organization requires more than installing antivirus software or deploying firewalls. It requires a documented, repeatable approach to managing human-related security risks.